Network Security Management: How To Secure Complex IT Infrastructures?

If you want to secure your data, then understanding network security management is a fundamental skill for securing your infrastructure against threats.
I notice that many professionals acquire firewalls and other network tools. But they continue to experience security incidents.
This outcome is expected because many organizations have implemented defensive solutions. However, these teams have failed to understand how to properly leverage the tools they purchase.
What Is Network Security Management?
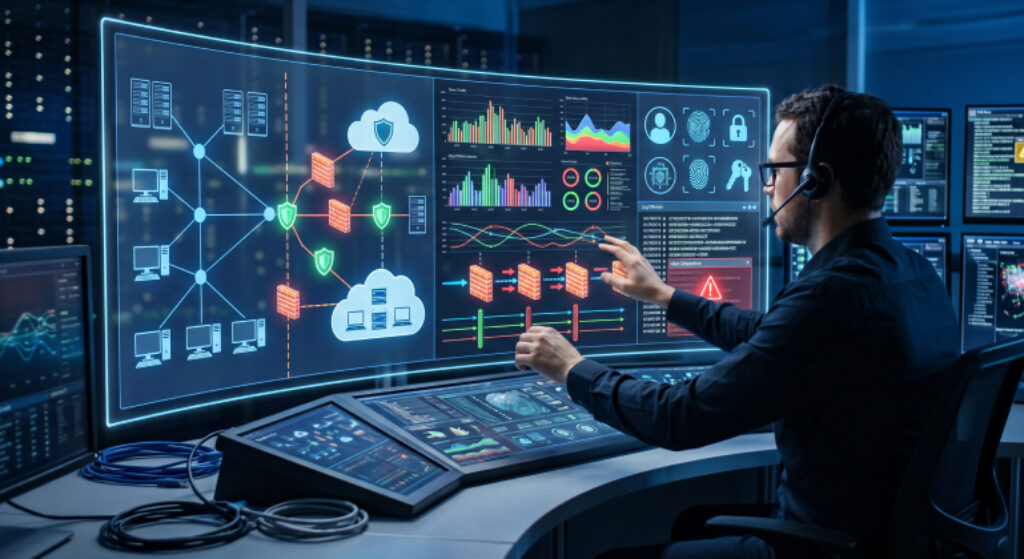
Network security management refers to the unified program that combines diverse elements such as:
- Firewalls.
- Access control.
- Other monitoring systems.
It is the practice that oversees the whole system by providing a dashboard that enables the IT department to track and protect data and systems under a single pane of glass in both cloud-based and local environments, thus countering cyber-attacks.
Network Security Management Essentials
Before we proceed to the best practices, it is critical to appreciate the components of network security management.
It is not enough to understand how these tools work because we need to develop an efficient strategy to secure our networks.
Many businesses use a combination of software and hardware to enforce network security policies. For example, organizations use centralized administration software to configure all their nodes with a single interface.
Firewalls are also utilized to filter incoming and outgoing data packets. In addition, firms implement identity and access management tools to protect their data.
The table below demonstrates the key components of network security management.
| Component | Primary Purpose | Impact on Risk Reduction |
| Centralized Console | Unifies disconnected tools | Eliminates operational blind spots |
| Automation Tools | Deploys patches and updates instantly | Neutralizes zero-day exploits quickly |
| Network Segmentation | Isolates critical subnets | Stops lateral threat movement |
| Continuous Monitoring | Tracks real-time traffic patterns | Lowers mean time to detect threats |
The Hidden Risks Of Policy Creep And Rule Fatigue In Network Security
When I examine the weaknesses in the cybersecurity framework of an organization, there are rarely insufficient tools.
Instead, I often observe excessive rules that have accumulated over time. This issue is known as policy creep and rule fatigue.
In many cases, administrators develop new rules to accommodate new vendors. As a result, organizations face hundreds of orphaned rules that create opportunities for malicious actors.
For example, some companies develop rules for temporary vendors, but they forget to delete these regulations after the contracts expire.
Similarly, security teams develop shadow rules to give access to developers. These rules are not subjected to the same scrutiny as the rest of the security policies.
In addition, some rules conflict with each other, thereby creating vulnerabilities. For example, some companies cannot establish a coherent set of rules for cloud and on-premises networks.
The table below compares the risks, causes, and solutions for rule fatigue:
| Risk Factor | Operational Cause | Management Solution |
| Accumulated Rules | Lack of strict rule expiration dates | Implement mandatory time-to-live attributes on exceptions |
| Configuration Drift | Manual, undocumented adjustments | Deploy change control management tracking systems |
| Alert Fatigue | Floods of low-context telemetry data | Set up behavior-based correlation filters |
Technical Debt In Encrypted Traffic Inspection
Modern networks utilize encryption to secure data packets. This encryption utilizes Transport Layer Security (TLS) protocols.
While encryption is a reliable security mechanism, it also tends to create single points of failure.
Attackers are also likely to use encryption to conceal malware. For example, there is a possibility that a threat actor might encode malware within an encrypted channel.
This attack vector is particularly dangerous because it will be challenging to separate legitimate data from malware.
There are three main issues with encrypted traffic inspection.
- First, many tools reduce the performance of networks when examining encrypted data packets.
- Second, decrypting data packets can expose confidential employee data to attackers.
- Finally, certificate management is a primary source of operational issues during inspection. For instance, if the local certificates expire, encrypted data packets will be unable to pass through the firewall.
The table below compares the inspection strategies.
| Inspection Strategy | Technical Advantage | Operational Challenge |
| Full SSL/TLS Decryption | Exposes hidden malware payloads inside payloads | Requires significant hardware processing power |
| Encrypted Traffic Analytics | Detects threat signatures without decryption | Relies heavily on complex heuristic modeling |
| Selective Decryption | Bypasses sensitive personal sites to ensure compliance | Demands constant, accurate domain categorization |
Related Article For You: Antivirus Reedoor2.4.6.8: Enhancing Digital Security While Optimizing Tasks
Management Of Security Tools In Cloud Infrastructure
Traditional infrastructure uses physical servers to host organizational data. The security measures are applied at the level of these physical servers.
Administrators can only manage these tools by examining their physical location or the Internet Protocol (IP) addresses.
Cloud infrastructure is significantly more complex because these virtual machines can be created and deleted within a few minutes. It is also challenging to examine the physical location of a cloud server.
Therefore, if we utilize these traditional tools in a cloud infrastructure, we will encounter several issues. We need to rethink our strategy so that these principles apply to cloud infrastructure.
The table below compares the concepts and their application in network security management.
| Cloud Native Concept | Application Method | Security Benefit |
| Infrastructure as Code | Standardize configurations via automated scripts | Prevents human configuration errors |
| Just-In-Time Access | Grant administrative privileges for limited windows | Minimizes the risk of account exploitation |
| Postural Telemetry | Scan cloud assets continuously for misconfigurations | Catches infrastructure drift instantly |
Best Practices In Proactive Network Security Management
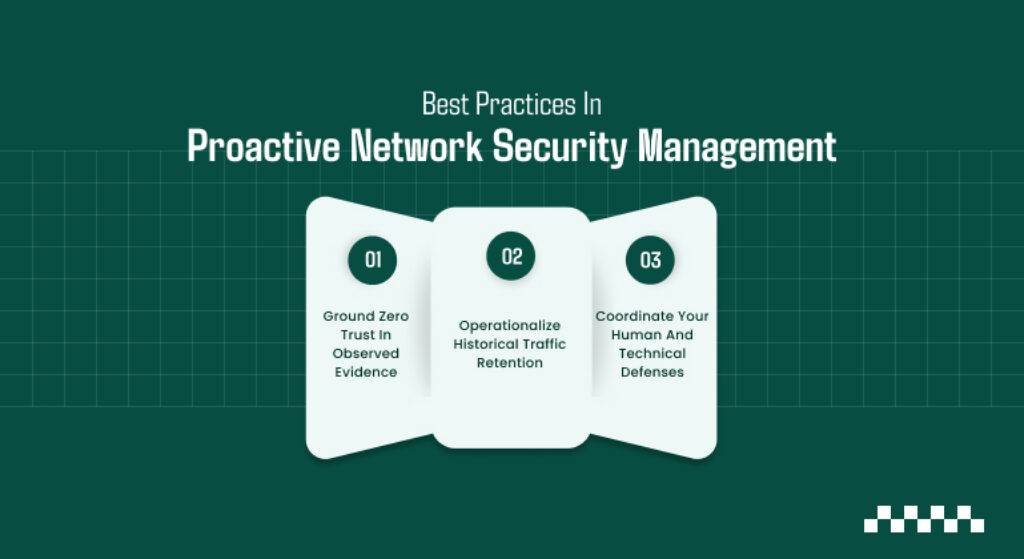
It is time to revisit the best practices in network security management. By implementing these recommendations, we can transform our cybersecurity framework into a proactive initiative. There are three key steps that we must consider.
1. Ground Zero Trust In Observed Evidence
Do not assume your zero trust architecture is working just because identity tokens match. You must validate access decisions against real traffic patterns.
- Compare user permissions against actual data access behaviors.
- Isolate endpoints immediately when traffic deviates from established baselines.
- Log every access attempt across on-prem, cloud, and hybrid nodes.
2. Operationalize Historical Traffic Retention
Attackers often maintain deep dwell time before executing a payload. You need historical network context to reconstruct the true timeline of a security breach.
- Retain high-value session data from your most critical data segments.
- Use packet captures to distinguish between benign software bugs and active exploits.
- Incorporate historical telemetry into your threat hunting workflows.
3. Coordinate Your Human And Technical Defenses
According to data compiled by NBM, human error precipitates roughly 95% of all cyberattacks. Your technical controls must complement rigorous operational training.
- Train your staff to recognize sophisticated, AI-driven phishing variants.
- Automate employee offboarding to eliminate risky orphaned accounts.
- Apply role-based data filters to reduce data exposure across your workforce.
Critical Technical Specifications For Tools Selection
It is time to select the appropriate tools for our network security management needs. We need to consider several requirements before selecting a specific technology. We must also ensure that the tools are compatible with our infrastructure.
The first requirement is the ability to operate multiple tenancy environments. It is possible that our organization needs to separate the responsibilities of different units. This observation is particularly applicable to organizations that utilize outsourced IT services.
The second technical requirement is the application programming interface (API). The network security management tools should be programmable so that we can develop automated scripts.
Finally, the tools must have a high throughput capacity. We must ensure that the tools can inspect data packets at the rate of our network traffic. The table below compares the technical requirements of network security management tools.
| Platform Feature | Enterprise Necessity | Small Business Necessity |
| Multi-Tenant Control | Essential for isolated business units | Helpful for outsourced IT providers |
| Behavioral AI Analytics | Crucial for separating signal from noise | Important for low-staff IT teams |
| Regulatory Mapping | Automates compliance reporting for audits | Lowers total compliance costs |
Choosing A Network Security Management System: Key Considerations
The selection process is the final stage in our guide to network security management. We need to ensure that the tools are compatible with our current workflow. It is possible that some tools cannot be utilized due to insufficient skills.
For instance, if the tools are too complicated for our system administrators, they will not be able to utilize their full potential.
| Selection Lens | High-Priority Requirement | Common Pitfall to Avoid |
| Infrastructure Fit | Complete coverage across your exact hybrid footprint | Buying a tool built exclusively for on-premise hardware |
| Analyst Efficiency | Built-in correlation workflows that reduce alert volume | Tool sprawl that forces analysts to jump between systems |
| Compliance Auditing | Immutable logs that generate instant, framework-specific evidence | Relying on temporary dashboards that overwrite historical traffic data |
There are three main criteria that we need to consider when selecting our tools. The first criterion is related to the coherence of telemetry data.
We must ensure that the tools can collect data from on-premises, Software as a Service (SaaS), and cloud infrastructure. In addition, we should look for tools that are not forced to use multiple console interfaces.
The second selection criterion is related to operational efficiency. We must select tools that can utilize correlation strategies. This requirement is important because it will reduce the workload of our security analysts.
Finally, we must ensure that the automation features can be reversed to avert operational downtime.